EXPERTISE
Safety of intended functionality.
A system can behave as designed and still create a hazard. We evaluate whether the intended functionality is sufficient for the situations it encounters, including limitations in sensing, interpretation, decision-making and interaction with users.
Define the conditions that matter
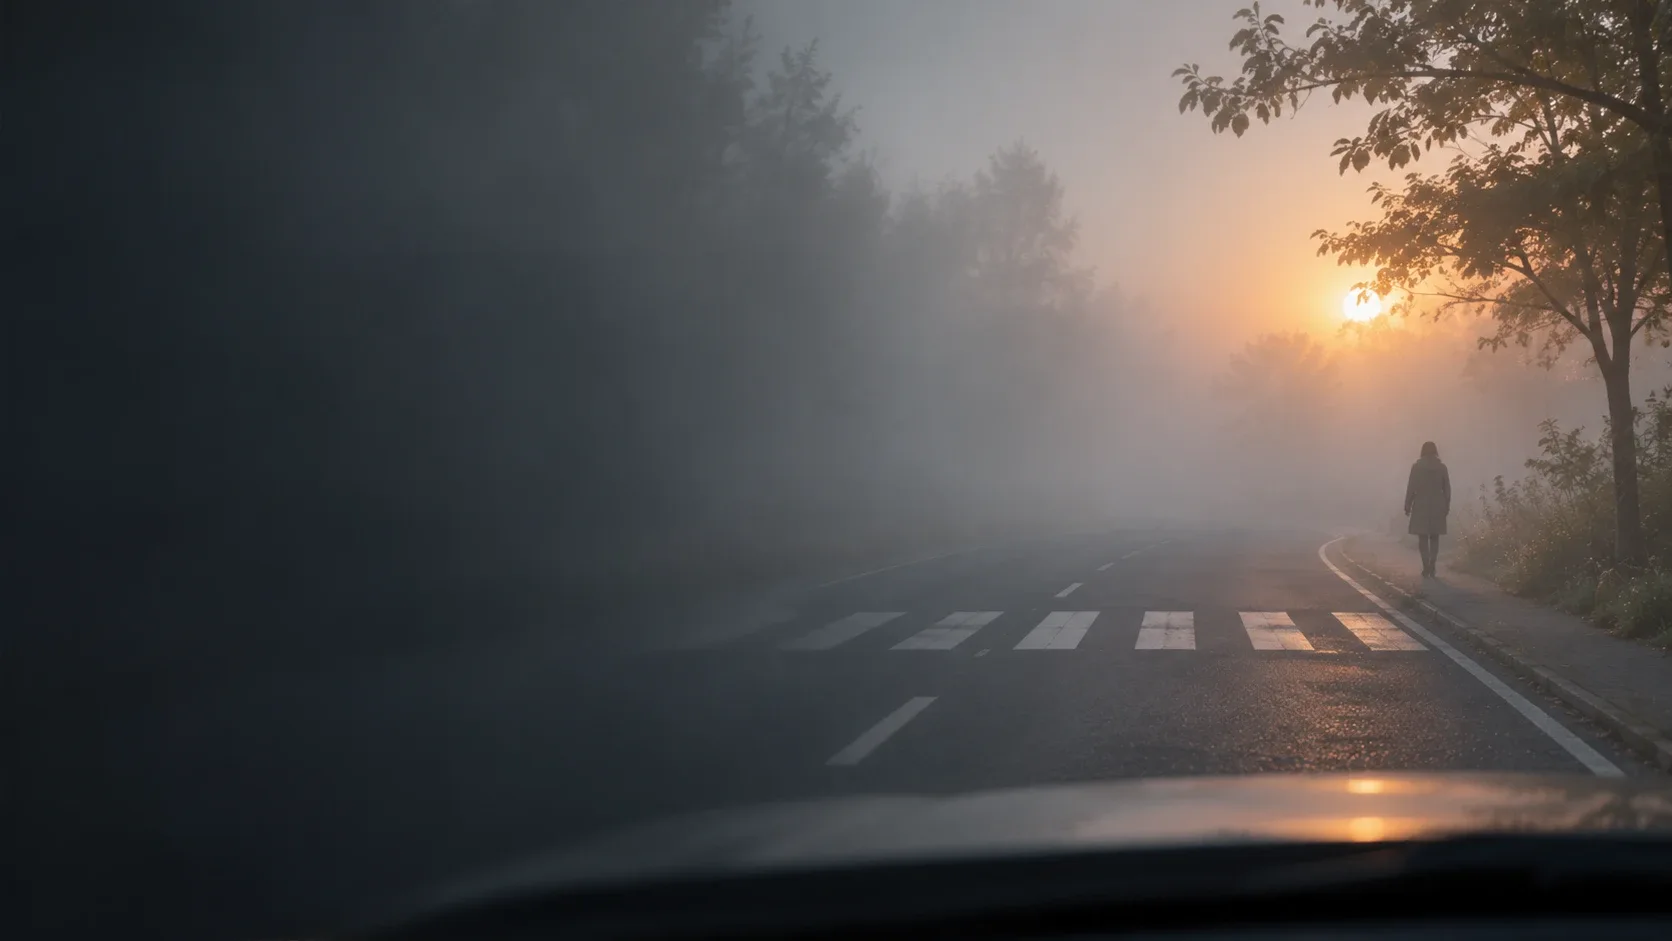
We examine the operational design domain, system assumptions and foreseeable misuse. Triggering conditions such as occlusion, glare, ambiguous objects or unexpected human behaviour help identify where otherwise functioning components can produce unsafe outcomes.
Build a justified validation strategy
Scenario selection, coverage arguments and acceptance criteria connect the known limitations to the test programme. We review simulation, controlled tests and operational evidence, making the representativeness and remaining gaps explicit.
Control the remaining exposure
Operating restrictions, monitoring, fallback and changes to the functionality can reduce exposure to hazardous conditions. We connect these controls to requirements and the safety argument, and review their adequacy as the design or environment changes.
STANDARDS & ENGINEERING REFERENCES
Relevant standards
We agree applicable standards, editions and assessment criteria for your product, operating environment and contractual obligations.
- ISO 21448 · SOTIF
- Safety of the intended functionality in road vehicles: functional insufficiencies, triggering conditions and validation.
ISO 21448 is an automotive standard. For robotics and other domains, we transfer relevant methods while establishing the actual applicable requirements separately.
These references describe our engineering scope; they are not claims of company or product certification. Browse all standards and their scope.
Bring your engineering question.
Tell us about your system, the decision ahead and the evidence you need. We’ll help define a useful next step.